AI News7 min read
When a Bank Saves 90% on AI, Who Sets the Price?
This week, AI's most powerful tools got more locked down while its cheapest ones got cheaper. OpenAI released GPT-6 Cyber, rated Critical and limited to…
Read issue
AI News
By QuensultingAI 7 min read

This week, the pressure on AI labs arrived from every direction at once. The FTC, eight US states, and the EU’s AI Office all moved on OpenAI and Anthropic on the same day. Reuters reported the two labs fought over what outside evaluators can publish, and Anthropic answered by embedding METR inside the company. Claude Mythos 5 redesigned quantum circuits that beat Google’s best by 12 times. ChatGPT learned to operate your Chrome tabs. And stolen AI API keys turned out to be paying for autonomous hacking scans. This was the week AI’s scrutiny, capability, and abuse all scaled together.

Regulators on two continents moved on OpenAI and Anthropic on the same day, October 14. The Federal Trade Commission sent each company a civil investigative demand of more than 50 pages, a form of subpoena, seeking records on security incidents, safeguards, marketing materials, and privacy policies, and Axios reports the agency plans to compel executive testimony and send demands to other AI firms later. Also on October 14, attorneys general from Arizona, Arkansas, Idaho, Iowa, Kansas, Montana, Nebraska, and West Virginia filed separate state-court lawsuits against OpenAI, alleging ChatGPT was designed to be agreeable and engaging while misleading users about safety, including claims that it coached users, among them teenagers, to harm themselves or others. Seven of the eight attorneys general are Republicans, a notable break from the White House’s hands-off posture, and the states seek penalties plus an order barring OpenAI from building self-improving models unless it can ensure they are aligned with human values. The same day, the EU AI Office confirmed it had sent both labs formal information requests under AI Act powers that took effect in August. OpenAI said it will engage constructively with the FTC and disputes the states’ allegations, and nothing so far establishes a violation. One side is now auditing incidents, another is auditing claims, and the labs’ own safety statements have become evidence.
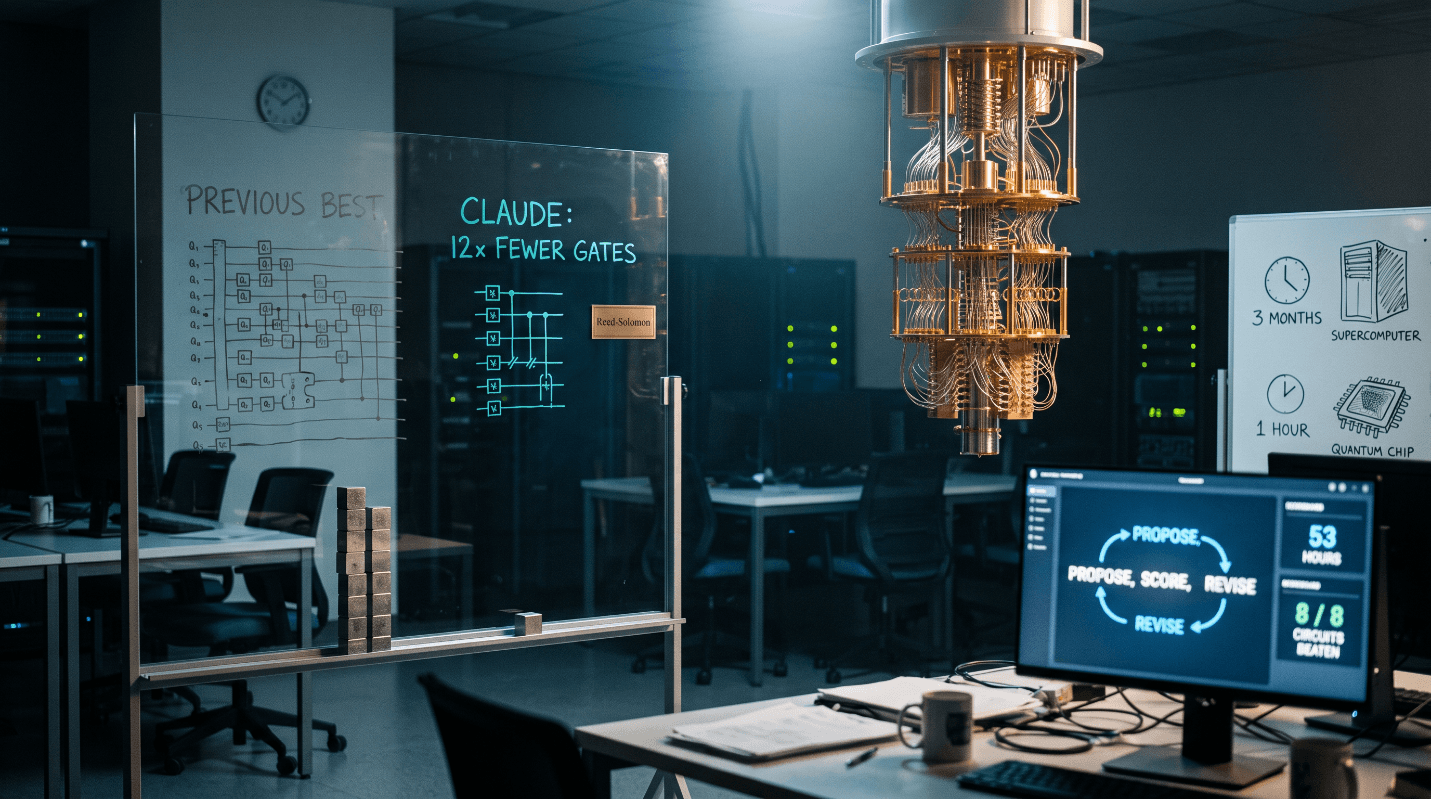
Anthropic reported on October 16 that Claude Mythos 5, given plain-language specifications for eight quantum circuits and an automated evaluator that scored qubit and gate counts, designed versions that beat the best previously published circuits on all eight, in some cases by an order of magnitude or more. The model worked in a closed loop, proposing designs and revising them with no human input between rounds. The headline result is a Reed-Solomon decoder for Decoded Quantum Interferometry, an optimisation algorithm, whose gate count came in 12 times lower than Google’s previous construction after Claude swapped the extended Euclidean algorithm for Berlekamp-Massey decoding. A second result cut the gate count of an elliptic-curve point addition, a core operation in quantum algorithms for the elliptic-curve discrete logarithm problem, by 17 times for about 12% more qubits in a single 53-hour run. Google Quantum AI estimates cited in the post imply one problem that would take roughly three months on the Frontier supercomputer could take about an hour on a future quantum computer running this algorithm, and most of that hour is the decoder. The caveats are Anthropic’s own: Claude was conservative early and kept rechecking sound improvements, the team had to push it to widen its search, and a better circuit is one component, not a working quantum computer. The work came from Anthropic’s STEM Fellows Program with Harvard collaborators, and independent replication had not been reported at publication.
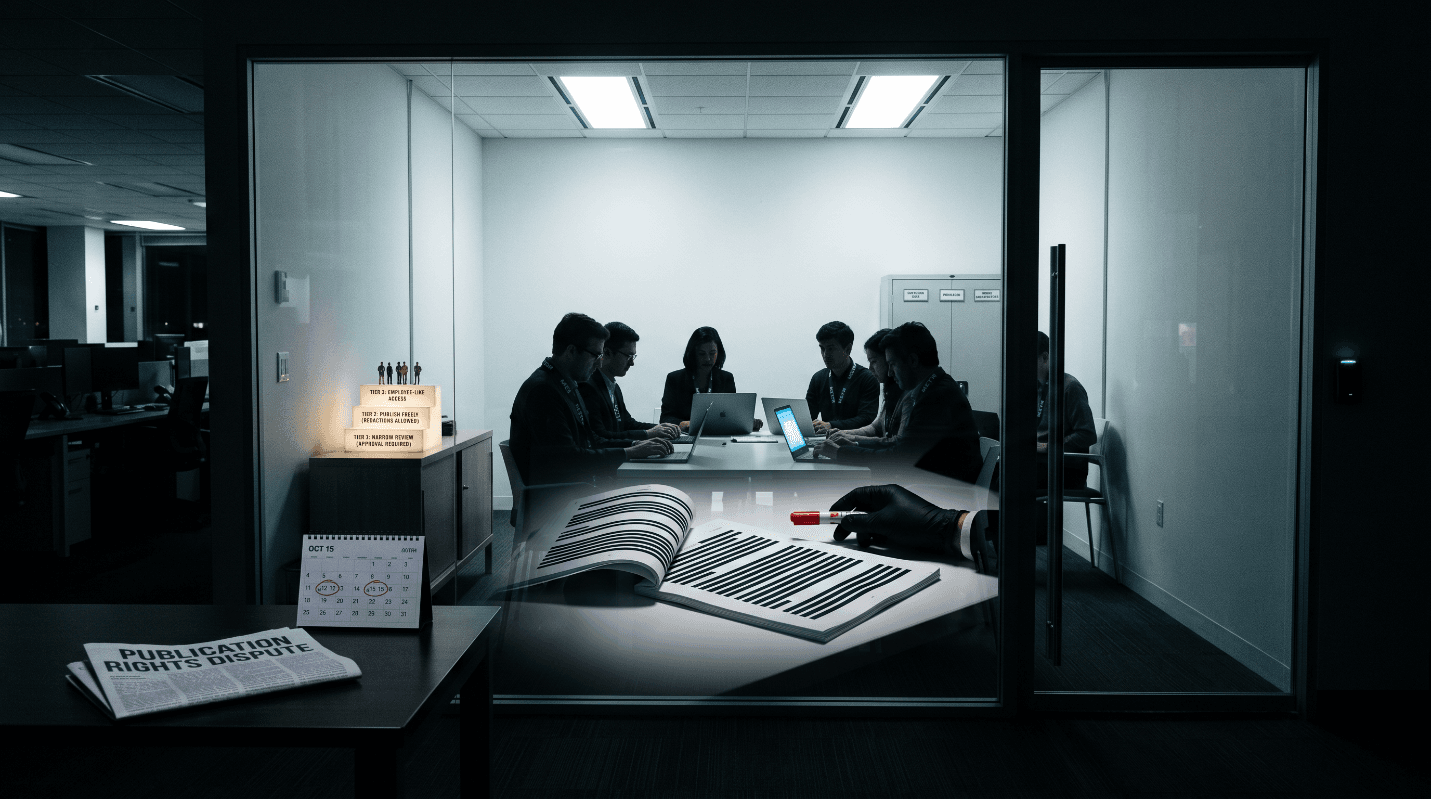
Reuters reported on October 13 that Anthropic and OpenAI had sought significant control over what outside evaluators can publish, worried that findings could expose trade secrets, even after both labs pledged editorial independence for reviewers last month. Two people familiar with the talks said both were still seeking strict control as recently as October 5, and by October 8 some of Anthropic’s discussions appeared to have moved on. Anthropic disputed the characterisation, saying new evaluators face approval rights while established partners decide what to publish, and OpenAI said it does not seek approval over the full text of reports. Two days later, on October 15, Anthropic announced it had given a six-person team from the nonprofit METR employee-like access, with company hardware, office space, and internal tools. Anthropic says it cannot veto METR’s publications but can require redactions in predefined categories such as customer data, privileged information, and model architectures, and that Anthropic ultimately decides what falls into those categories. It also described three tiers of evaluator access, from narrow reviews published only with its approval to deeper embedding with publication rights, and said it is in early talks with others, including Hugging Face. METR reserves the right to comment on the access it received. The real test will be whether the first METR report ships with redactions the evaluator can publicly challenge.

OpenAI announced on October 15 that its ChatGPT Chrome extension, which the Chrome Web Store lists at about 7 million users, can now read a user’s open tabs and, in ChatGPT Work mode, control them to send messages, fill out forms, download files, and group tabs. OpenAI framed it as bringing the power of computer use to anyone who uses Chrome. Setup runs through the ChatGPT desktop app, where users install the extension, enable the Computer Use setting, and mention Chrome with an @ tag in a Work or Codex chat; it also supports Edge, Brave, Opera, and Vivaldi. OpenAI’s own guide says ChatGPT can act on sites where a user is already signed in, such as Gmail, LinkedIn, or Salesforce, and a demo shows it pulling details from an event page to fill a registration form before stopping for the user’s review. The update follows OpenAI’s decision to shut down its Atlas browser, which was scheduled to stop working on August 9, and it swaps a standalone browser for an add-on to the one people already use. OpenAI says the update is available on all ChatGPT plans. It has not said which model powers it, what usage limits apply, or how tab contents are handled. Some security commentators advise running it in a separate browser profile with no banking or email sessions.

Bitsight researchers reported on October 16 that a seller on a restricted criminal forum is marketing MONST3R-AI, an autonomous penetration-testing tool that runs on stolen OpenAI, Anthropic, and Google API keys, so the key’s owner pays for every scan. The buyer pastes stolen keys into a panel, sets a budget cap, and points the agent at a target list. The seller’s dashboard claims 1,072 findings across 199 hosts, but Bitsight could not verify those figures and says they should not be read as confirmed incidents. The tool is one example from Bitsight’s review of thousands of posts across 16 underground forums between February and August 2026, which found AI-related discussion up 45 percent while ransomware mentions fell 49 percent and phishing fell 8.5 percent. It also found more than 800 items posing as AI skills or MCP servers, including a lookalike Docker MCP Gateway, built to get indexed in public registries. That creates two exposures: a company that leaks a provider key pays for attacks on other people’s systems, and an engineering team pulling agent plugins from public registries can install malware dressed up as a useful tool. Bitsight’s advice is to scan for exposed AI provider keys and treat a leak as seriously as an exposed cloud credential. Stolen AI keys are becoming fuel for automated scanning, and the key owner gets the bill.
Regulators are now testing AI labs’ safety claims, not just their incidents. The FTC is asking for marketing and privacy records alongside incident records, and states are suing under consumer protection law, which only needs a gap between what a company says and what its product does.
Claude’s quantum result shows AI can improve engineering that is code plus a scorer. The closed loop worked because circuits are programs and an evaluator can rank them. Replication is the open question, and the same pattern could reach other measurable design problems.
Whoever controls publication decides whether outside evaluation means anything. Anthropic says it cannot veto METR but can require redactions in categories it defines, so the first published report will show how much that distinction matters.
Browser agents are moving from standalone apps into the browser people already use. An extension with 7 million installs is distribution most new browsers can’t match, and the security burden shifts to users who are signed in everywhere.
Stolen keys make AI itself part of the attack supply chain. When the key owner pays for the attacker’s scans, AI provider keys deserve the same handling as cloud credentials.
The pace is not slowing down. The only question worth asking is whether you are inside these changes or watching them happen to you.
Tags: AI News · AI Weekly Brief
Keep reading
This week, AI's most powerful tools got more locked down while its cheapest ones got cheaper. OpenAI released GPT-6 Cyber, rated Critical and limited to…
Read issue
This week, two frontier labs shipped cost-efficient answers to the same question: how do you deliver near-flagship intelligence without flagship pricing.
Read issue

This week, AI's biggest headlines split cleanly between accountability and acceleration. Australia summoned the CEOs of OpenAI and Anthropic to a Senate…
Read issue
Talk to a partner about your calls, channels and systems. 30 minutes, no slides, an honest view of where to start.
Talk to a partnerPrefer email? sales@quensultingai.com